
Small Business Compliance in 2026: 7 Challenges, the Tools to Buy, and the Workflows to Automate
Small business compliance in 2026: seven areas, current rules, real penalties, Vanta, Drata and Secureframe pricing, and which workflows AI agents can automate.
A US small business in 2026 has to cover seven compliance areas: labor law, tax, data privacy, healthcare privacy, financial audit, payment security and workplace safety. This guide gives the current rules and real penalties, says when a platform such as Vanta, Drata or Secureframe is worth buying, and names the workflows an AI agent can run with a person approving.
TL;DR: The 7 Compliance Areas Every Small Business Must Cover in 2026
If you run a small business in the US in 2026, you are on the hook for more compliance work than any previous generation of founders.
- Labor Law Compliance (EEOC, Department of Labor, FLSA, state wage and hour laws)
- Tax Compliance (IRS federal, state sales tax, 1099 NEC for contractors)
- Data Privacy (CCPA, CPPA, Washington My Health My Data, GDPR for EU customers)
- Healthcare (HIPAA for any business that handles PHI)
- Financial Audit (SOX-lite for investor-backed SMBs, GAAP for anyone raising)
- Payment Security (PCI DSS 4.0.1 for anyone taking cards)
- Workplace Safety (OSHA for physical workplaces)
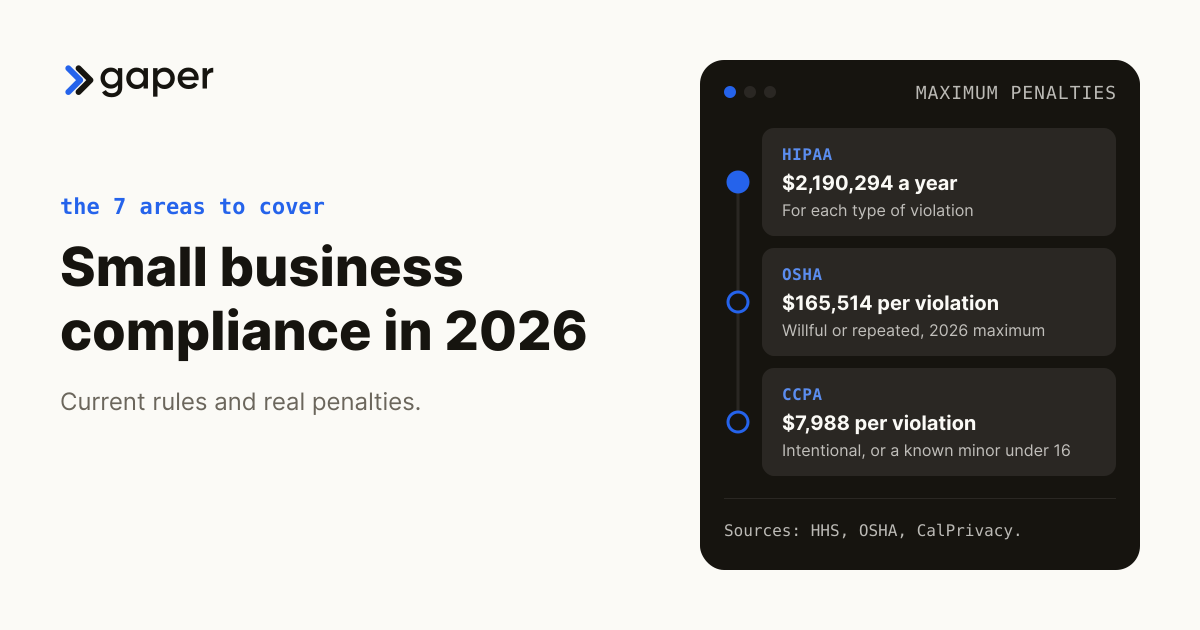
Non compliance is expensive. HIPAA civil penalties can reach $2,190,294 per year for each type of violation. EEOC settlements announced in 2026 with three named employers, among them a coffee company and a home health agency, ran from $22,500 to $45,000 per case. OSHA penalties reach $165,514 per willful violation.

Table of Contents
- What Does Small Business Compliance Mean in 2026?
- The 7 Biggest Compliance Challenges for Small Businesses
- Real 2025 to 2026 Penalty Data (Why Compliance Matters)
- The Top Compliance Tools for Small Businesses (2026 Comparison)
- Compliance Tools Comparison Matrix
- When should a small business buy a compliance tool?
- How AI Agents Automate the Repetitive Compliance Work
- Which compliance workflows can an AI agent run with a person approving?
- How Gaper Builds Custom Compliance AI for SMBs
- What are the seven compliance areas every US small business must cover in 2026?
- How much does compliance software like Vanta or Drata cost?
- What is the best compliance software for SMBs?
- Can AI agents automate compliance work for SMBs?
- Does an early-stage startup actually need SOC 2 compliance?
- How expensive can non-compliance penalties be for a small business?
- What happens if my small business is not compliant?
Drowning in compliance work?
AccountsGPT handles audit trails automatically. Agent Kelly handles HIPAA aware scheduling. Gaper builds custom compliance AI in 2 to 8 weeks.
What Does Small Business Compliance Mean in 2026?
It means following the federal, state and industry rules that govern how you hire, pay, sell, store data, take card payments and run your workplace, and being able to prove it to a regulator, an auditor or a customer.
Small business compliance in 2026 means staying in alignment with federal, state, and industry specific regulations that govern how you hire, pay, sell, store data, handle payments, and operate your physical or digital workplace. A non compliant SMB faces fines, lawsuits, lost deals (because enterprise buyers refuse to work with non-compliant vendors), and reputational damage. The good news is that compliance automation tools have gotten dramatically better, and AI agents can now handle the repetitive compliance work that used to drain your operations team.
Size decides which rules apply. Title VII and the ADA cover employers with 15 or more employees, federal age discrimination law 20 or more (EEOC), and the FMLA 50 or more (DOL). The FLSA, payroll tax and PCI DSS have no headcount minimum.
Why Compliance Got Harder in 2025 to 2026
Five shifts happened between 2024 and 2026 that increased the compliance burden on small businesses.
First, state privacy laws multiplied. The IAPP's chart, updated 8 September 2026, lists 23 states with signed comprehensive privacy laws, 19 of them in effect, with Indiana, Kentucky and Rhode Island starting on 1 January 2026 (IAPP). Each has slightly different definitions and penalty structures. Second, the Washington My Health My Data Act went into effect on 31 March 2024 (30 June 2024 for small businesses) with broad health data definitions. Third, the EU AI Act phased in: bans from 2 February 2025, general-purpose AI rules from 2 August 2025, and, after the Digital Omnibus on AI (adopted June 2026), stand-alone high-risk obligations from 2 December 2027 (European Parliament legislative train). Fourth, the future-dated requirements of PCI DSS 4.0.1 became mandatory on 31 March 2025. Fifth, the IRS changed 1099 rules twice: from 2024 anyone filing 10 or more information returns must e-file, and for 2026 payments the 1099-NEC threshold rose from $600 to $2,000 (IRS instructions for Forms 1099-MISC and 1099-NEC).
California added a sixth: rules on risk assessments, automated decisionmaking technology and cybersecurity audits took effect on 1 January 2026 (CalPrivacy).
The 7 Biggest Compliance Challenges for Small Businesses
1. Labor Law Compliance (EEOC, DOL, FLSA)
Labor law touches every business with employees. Main federal pieces: FLSA (minimum wage, overtime, classification), Title VII (anti-discrimination), ADA (accommodation), FMLA (protected leave for 50+ employees), state wage and hour laws. The most common SMB failures are misclassifying employees as contractors, missing overtime pay, and poorly documented termination decisions.
The federal minimum wage is still $7.25 an hour, and many states set more. The salary floor for the white-collar overtime exemption is $684 a week ($35,568 a year), since a court vacated the 2024 increase; the DOL removed that rule on 15 May 2026 (Federal Register). Contractor classification is in flux: the DOL proposed rescinding its 2024 independent contractor test on 27 February 2026, but it is not final: the 2024 rule governs private suits, though DOL investigators dropped it in May 2025 (Federal Register; DOL).
The EEOC publishes no average settlement for small businesses, but in fiscal year 2025 it secured $660 million for 17,680 people (EEOC).
2. Tax Compliance (IRS, State Sales Tax, 1099 NEC)
Federal income tax, payroll tax (quarterly), state sales tax (post-Wayfair economic nexus), and 1099 NEC for contractors. The 1099-NEC threshold is $600 for payments made in 2025 (filed in early 2026) and $2,000 for payments made in 2026, with inflation adjustments possible from 2027. Form 1099-K reporting is back to more than $20,000 across more than 200 transactions (IRS).
Missing a 1099 filing triggers a $340 penalty per form (filed after 1 August or never, returns due in 2026 and 2027). Filing within 30 days costs $60 per form, by 1 August $130, and intentional disregard $680 for 2026 returns (IRS information return penalties).
Most common SMB failures: missing state sales tax obligations after crossing nexus thresholds, misclassifying contractors, late quarterly payroll tax deposits. A common nexus trigger is $100,000 in sales into a state, and states keep dropping the second test of 200 transactions: Illinois dropped it on 1 January 2026 (Illinois Department of Revenue). Check each state's own revenue department page. On the bookkeeping side, AccountsGPT, Gaper's accounting agent, does tax preparation and payroll.
3. Data Privacy (CCPA, CPPA, Washington My Health My Data, GDPR)
The fastest growing compliance area. The CCPA applies only above set thresholds. It covers a for-profit business in California with annual gross revenue of $26,625,000 or more, or that buys, sells or shares data on 100,000 or more California residents or households, or earns 50 percent or more of revenue from selling or sharing it (CalPrivacy FAQ). Fines run up to $2,663 per violation and $7,988 per intentional violation or one involving a known minor under 16 (CalPrivacy).
The 2025 California rules add three duties: risk assessments from 1 January 2026, with attestations due by 1 April 2028; the automated decisionmaking rules from 1 January 2027; and cybersecurity audit certifications due on 1 April 2028, 2029 or 2030 by revenue (CalPrivacy, 23 September 2025).
Washington My Health My Data Act has broad health data definitions, and a violation is a violation of the state Consumer Protection Act, so the Attorney General can seek civil penalties of up to $7,500 per violation and consumers can sue (Washington Attorney General; penalty). Colorado, Virginia, Connecticut, Texas and others each have their own rules. GDPR reaches non-EU firms selling to or tracking people in the EU, with fines up to 20 million euros or 4 percent of global annual turnover, whichever is higher (GDPR Articles 3 and 83).
4. Healthcare (HIPAA for Any Business Handling PHI)
HIPAA applies to health plans, clearinghouses and most healthcare providers AND their business associates (cloud, billing and software vendors handling their PHI). Even an accounting firm can be in scope: in August 2025 HHS settled a ransomware case with BST & Co. CPAs, LLP for $175,000 (HHS). HIPAA requires administrative, physical, and technical safeguards, a business associate agreement with every vendor that touches PHI, and, for covered entities, breach notice to affected people no later than 60 calendar days after discovery.
Fines are tiered. HHS's 28 January 2026 adjustment sets $145 to $73,011 per violation at the lowest tier and up to $2,190,294 at the highest, with a $2,190,294 calendar-year cap for identical violations, unchanged for 2026 (Federal Register; HHS). Criminal penalties for knowing violations can reach $250,000 and 10 years in prison when committed for gain or malicious harm (42 USC 1320d-6).
One change is still pending. HHS proposed a major Security Rule update on 6 January 2025, and the latest regulatory agenda lists it as a long-term action with final action targeted for July 2027 (reginfo.gov). The current rule already expects a written risk analysis, and OCR's 2025 settlements with Vision Upright MRI, Comstar and Regional Women's Health Group each cite a missing or inadequate one.
5. Financial Audit (SOX-lite for Investor Backed SMBs)
Full SOX applies to public companies, but investor-backed private companies face SOX-lite expectations. Many venture capital and private equity investors expect portfolio companies to maintain SOX-like controls: documented financial controls, segregation of duties, audit trails, annual external audit. Most common failure: not keeping an audit trail on financial transactions, which causes problems at the next funding round.
SOX-lite is not a law, so no regulator fines you for missing it. The cost shows up in diligence, when a buyer who cannot trace numbers to source documents lowers the price or walks away.
6. Payment Security (PCI DSS 4.0.1)
PCI DSS applies to every business that stores, processes, or transmits credit card information. Version 4.0.1 is the current standard: version 4.0 was retired on 31 December 2024, and the future-dated requirements became mandatory on 31 March 2025 (PCI SSC; dates). If you use Stripe, Square, or Braintree, they handle most of the PCI burden, but you still have obligations, usually an annual self-assessment questionnaire. If you run your own payment infrastructure, PCI DSS 4.0.1 is a serious operational burden.
The PCI Security Standards Council does not fine anyone; penalties come from the card brands and acquiring banks (PCI SSC), and the Council publishes no fine schedule, so treat any dollar range as an estimate.
7. Workplace Safety (OSHA)
OSHA regulates workplace safety for physical workplaces. Recent focus: heat illness prevention, ergonomics, workplace violence prevention. Maximums in force for 2026: serious violation $16,550, willful or repeated $165,514, failure to abate $16,550 per day. These are the 2025 amounts (Federal Register): the 2026 inflation adjustment was cancelled because the October 2025 price data it needs was never published (Federal Register, 27 May 2026).
There is still no federal heat standard: OSHA proposed one in August 2024, and its agenda targets a supplemental proposal for December 2026 and final action for October 2027 (reginfo.gov). States that run their own OSHA-approved plans can set stricter rules, so check yours.
Real 2025 to 2026 Penalty Data (Why Compliance Matters)
Abstract penalty ranges do not motivate action. Real enforcement examples do. Every row below is a named case from the regulator's own announcement.
| Area | Real Example | Fine |
|---|---|---|
| EEOC | Security Assurance Management, Inc., pregnancy and sex discrimination suit (February 2026) | $45,000 |
| EEOC | Mid-Michigan Home Health & Hospice LLC, race discrimination and retaliation (November 2026) | $41,137 |
| HIPAA | Vision Upright MRI, a one-facility imaging provider: no risk analysis, breach notice later than 60 days (May 2025) | $25,000 |
| HIPAA | Comstar, LLC, an ambulance billing business associate: ransomware, no thorough risk analysis (May 2025) | $75,000 |
| OSHA | Orchids Builders LLC, Florida roofing contractor, two willful and four repeat violations, mainly fall protection, proposed (July 2026) | $349,754 |
| CCPA | Todd Snyder, clothing retailer whose opt-out portal failed to process requests for 40 days (May 2025) | $345,178 |
HIPAA violation fines can reach $2,190,294 per violation category per year.
Criminal penalties for knowing violations can reach $250,000 and 10 years in prison.
The pattern: both HIPAA cases turn on a missing or inadequate risk analysis, and the CCPA case on a broken web form that a weekly automated test would catch.
The Top Compliance Tools for Small Businesses (2026 Comparison)
The three platforms below automate security and privacy frameworks. None publishes prices, so the figures here come from Vendr's buyer data (last updated February 2026), which reports what customers paid.
Vanta (SOC 2, ISO 27001, HIPAA)
A widely used SOC 2 automation platform for startups. Continuously monitors cloud infrastructure for compliance gaps, generates audit-ready evidence. Plans are Essentials, Plus, Professional and Enterprise, and Vanta now sells a "Vanta AI Agent" and agentic evidence checks (Vanta pricing). Frameworks include PCI DSS, GDPR, US state privacy, ISO 42001 and the EU AI Act (Vanta frameworks). Price: Vendr reports a median of $20,000 per year, with deals from $7,500 to $57,163 (Vendr). Best for Series A+ SaaS companies pursuing SOC 2.
Drata (SOC 2, ISO 27001, PCI, HIPAA)
Competes directly with Vanta. Plans are Foundation, Advanced and Enterprise; Foundation includes one framework, such as SOC 2 or HIPAA, and higher plans any of its 30+ frameworks, including PCI DSS and CCPA (Drata pricing; Drata frameworks). Drata also markets agentic AI for risk scoring and vendor reviews. Price: Vendr reports a median of $24,934 per year, with deals from $9,415 to $68,250 (Vendr). Best for SMBs pursuing multiple frameworks at once.
Secureframe (Compliance Automation)
Comparable automation to Vanta and Drata. Plans are Fundamentals, Complete and Defense (for CMMC), with Comply AI and a Secureframe Agent, and frameworks including PCI DSS, HIPAA, GDPR and CCPA (Secureframe pricing; Secureframe frameworks). Price: Vendr reports a median of $20,000 per year, with deals from $7,733 to $32,575 (Vendr). Best for growing SMBs that want a slightly lower-cost Vanta alternative: same median, lower ceiling.
AccountsGPT (Audit Trail and Financial Compliance)
Gaper's AI accounting agent that handles financial audit trail generation, SOX-lite compliance controls, and automated reconciliation. Price varies by deployment but starts meaningfully below traditional SOC 2 platforms for the financial side. Best for SMBs that need financial audit trails for investors or acquirers but are not pursuing SOC 2. See the AccountsGPT page for what it covers.
Compliance Tools Comparison Matrix
| Tool | Entry Price | Top Price | Frameworks |
|---|---|---|---|
| Vanta | $7,500/yr (Vendr low) | $57,163/yr (Vendr high) | SOC 2, ISO 27001, HIPAA, GDPR, US state privacy, PCI DSS, ISO 42001 |
| Drata | $9,415/yr (Vendr low) | $68,250/yr (Vendr high) | SOC 2, ISO 27001, PCI, HIPAA, GDPR, CCPA, ISO 42001 |
| Secureframe | $7,733/yr (Vendr low) | $32,575/yr (Vendr high) | SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR, CCPA |
| Bright Defense | $12,000/yr ($1,000/mo, published) | $36,000/yr ($3,000/mo, published) | SOC 2, ISO 27001, HIPAA, PCI DSS, CMMC (managed service) |
| AccountsGPT | Custom | Custom | Financial audit trail, SOX-lite |
Bright Defense is a managed service, not software; its tiers of $1,000, $2,000 and $3,000 a month cover 10 employees or fewer and one framework (Bright Defense, updated 28 September 2026).
Which Tool Fits Which Business
- Pre-seed startup: nothing yet (do not pay for SOC 2 until enterprise customers ask), or a managed service such as Bright Defense once the first request lands
- Seed to Series A SaaS pursuing SOC 2: Vanta or Drata
- Healthcare SMB needing HIPAA: Vanta, Drata or Secureframe all list HIPAA; Drata's Foundation plan can be bought for HIPAA alone
- E-commerce taking cards: first confirm what your processor covers; if you still need a platform, all three list PCI DSS
- Investor-backed SMB needing audit trails but not SOC 2: AccountsGPT + basic cloud controls
Need audit trails without paying for full SOC 2?
AccountsGPT handles SOX-lite and financial audit trails automatically. Gaper builds custom compliance AI in 2 to 8 weeks.
When should a small business buy a compliance tool?
Buy a platform when someone outside the company needs evidence you cannot produce from spreadsheets: an enterprise buyer asks for a SOC 2 report, you need two or more frameworks, or your cloud setup changes too often to check by hand.
Three signals mean it is time:
- A deal depends on it. A security questionnaire asks for a SOC 2 report or ISO 27001 certificate.
- You need more than one framework. Shared controls and one evidence store save real hours.
- Your infrastructure moves weekly. New cloud accounts, staff and vendors appear faster than anyone reviews them.
Do not buy one for the rest of this list: none of these platforms files a 1099, tracks sales tax nexus, checks overtime or keeps an OSHA log. Those workflows live in payroll, accounting and HR systems, where custom automation usually pays first. And the SOC 2 report itself comes from a CPA firm, so budget the audit fee on top. Our build vs buy guide covers the same decision for AI agents.
How AI Agents Automate the Repetitive Compliance Work
AccountsGPT for Audit Trails and SOX-lite
Financial compliance is mostly repetitive work: categorizing transactions, generating reports, flagging anomalies, maintaining audit trails. AccountsGPT handles all of this automatically. Every transaction categorization is logged with model version, rule, and confidence score. Draft reports are generated for human review. Audit queries can be answered with a few clicks. For an SMB with 500 to 5,000 transactions per month, AccountsGPT typically saves 40 to 80 hours of bookkeeping work per month.
That log answers a diligence team's first question: who made each entry, under which rule. More on finance workflows is in our guide to AI agents for accounting.
Agent Kelly for HIPAA Aware Healthcare Scheduling
For healthcare SMBs, Agent Kelly is Gaper's AI scheduling agent. Kelly is HIPAA-aware by design: patient data does not leave the clinic's compliant systems, scheduling decisions are logged for audit, and changes affecting multiple providers require human approval. Scheduling operations become HIPAA-compliant automatically.
The Kelly page and our guide to AI agents for healthcare show how it fits a clinic's front office.
Custom AI Agents for Labor Law Monitoring
Gaper's engineers build custom AI agents for specific compliance use cases: an agent that monitors employee time records and flags FLSA overtime violations, an agent that scans contractor invoices and flags misclassification risks. These are 2 to 8 week custom projects with clear ROI for SMBs with compliance exposure.
Which compliance workflows can an AI agent run with a person approving?
The repetitive, rule-based ones: tracking thresholds and deadlines, drafting filings and reports, routing privacy requests, and flagging overtime or contractor risks. A person approves anything filed, sent to a regulator, or decided about an individual.
Each workflow has a step the agent runs and a step a named person owns; our guide to human-in-the-loop AI covers those approval gates.
| Workflow | What the agent runs | What a person approves |
|---|---|---|
| 1099-NEC tracking | Totals vendor payments, flags vendors crossing $2,000 for 2026 payments, collects missing W-9s | The final filing list and the submission |
| Contractor classification | Scans invoices and work patterns for signs of employment | Any reclassification decision |
| FLSA overtime | Compares time records with pay and exemption status every pay period | Back pay and exemption changes |
| Sales tax nexus | Tracks sales by state against each state's threshold | Registering in a new state |
| CCPA requests | Logs delete and access requests, finds the records, drafts the reply inside the 45 calendar day window (CalPrivacy FAQ) | Identity checks on edge cases and the final response |
| HIPAA vendor list | Keeps the vendor inventory, flags vendors without a signed business associate agreement | Signing or ending a vendor relationship |
| SOC 2 evidence | Collects screenshots, access reviews and logs on schedule | Exceptions and the auditor's questions |
| Deadline calendar | Builds the federal and state filing calendar and sends reminders | Sign-off that each item was done |
Every agent action goes to a readable log, and anything that leaves the company waits for a named approver. Our note on AI agent security covers access controls for agents that touch financial and health data.
How Gaper Builds Custom Compliance AI for SMBs
Gaper.io in one paragraph
Gaper.io is a platform that builds and deploys production AI agents for business operations. Founded in 2019 and backed by Harvard and Stanford alumni, Gaper offers four named AI agents (Kelly for healthcare scheduling, AccountsGPT for accounting, James for HR recruiting, Stefan for marketing operations) plus engineering teams that build custom agents your business owns.
Gaper is the AI-native implementation partner that deploys supervised AI agents you own.
Many engineers in the Gaper pool have shipped production AI systems for regulated industries. The pool includes specialists who understand SOC 2, HIPAA, GDPR, CCPA, PCI DSS 4.0, and SOX-lite requirements from real production deployments.
Stop losing enterprise deals to compliance gaps.
AccountsGPT for finance. Agent Kelly for HIPAA. Custom compliance AI in 2 to 8 weeks.
Free 30 minute compliance automation scoping. No obligation.
14 verified Clutch reviews. Harvard and Stanford alumni backing. No commitment.
What are the seven compliance areas every US small business must cover in 2026?
Labor law (EEOC, DOL, FLSA), tax compliance (IRS, state sales tax, 1099 NEC), data privacy (CCPA, state privacy laws, GDPR), healthcare (HIPAA), financial audit (SOX-lite for investor-backed SMBs), payment security (PCI DSS 4.0.1), and workplace safety (OSHA).
Not every area applies to every business: HIPAA applies only if you handle PHI, OSHA's rules bite hardest in physical workplaces, and federal anti-discrimination law starts at 15 employees.
How much does compliance software like Vanta or Drata cost?
None of the three vendors publishes prices. Vendr's buyer data puts the median at $20,000 a year for Vanta and Secureframe and $24,934 for Drata, and Bright Defense's managed service lists $12,000 to $36,000 a year.
Deals range from $7,500 to $68,250 a year, scaling with headcount, frameworks and add-ons, and the CPA firm's audit fee is billed separately. SMBs that only need basic audit trails and financial compliance can use AccountsGPT from Gaper at a meaningfully lower total cost.
What is the best compliance software for SMBs?
For SOC 2, Vanta or Drata are the top picks. All three major platforms list HIPAA and PCI DSS, so choose on price, auditor fit and the frameworks you will need next year rather than on the label.
Drata's entry plan suits a company needing one framework, and Secureframe's price range tops out lowest. For lower cost managed service SOC 2, Bright Defense targets the smaller end of the SMB market, with tiers for 10 employees or fewer. For financial audit trails and SOX-lite without full SOC 2, AccountsGPT is a strong fit.
Can AI agents automate compliance work for SMBs?
Yes, for the repetitive portions like financial audit trail generation, transaction categorization, contractor classification monitoring, and deadline tracking. The deployments that work keep a person approving every judgment call.
AI agents can automate financial audit trail generation, transaction categorization, access review documentation, contractor classification monitoring, and regulatory deadline tracking. What AI cannot automate is the judgment calls: whether a worker is an employee, whether a breach must be reported. Most successful deployments are human-in-the-loop: AI handles the repetitive work, humans handle the judgment.
Does an early-stage startup actually need SOC 2 compliance?
Not until enterprise customers ask for it during procurement or you expect enterprise sales within six months. For pre-seed and seed startups without enterprise deals, SOC 2 is premature.
Start thinking about SOC 2 when you have 10+ enterprise prospects in your pipeline, start the actual process when your first enterprise deal requests it, and plan for several months from start to a first report. A Type 1 report checks your controls on a single date; a Type 2 report also tests whether they worked over an observation period your auditor sets, so it takes longer.
How expensive can non-compliance penalties be for a small business?
HIPAA civil penalties reach $2,190,294 per violation category per year, OSHA willful violations cost up to $165,514 each, and an unfiled 1099 costs $340 per form.
Smaller cases add up too: an EEOC religious discrimination case against a New York coffee company settled for $22,500 in 2026 (EEOC), and CCPA fines of up to $2,663 per violation multiply with every affected consumer.
What happens if my small business is not compliant?
Consequences range from a warning letter to six figure fines, lawsuits and lost enterprise deals. Most cases start with a complaint, a breach or a customer's security review.
Real 2025 to 2026 examples: $25,000 for an imaging provider with no HIPAA risk analysis, $349,754 in proposed OSHA penalties for repeated fall protection failures, and $345,178 under the CCPA for a broken opt-out portal. Beyond direct financial penalties, non compliance blocks enterprise deals and creates reputational damage. OSHA offers free compliance assistance, and fixing a gap before an inspection is cheaper than after.
Thirty minutes, no commitment. We map one workflow, make the build or buy call, and scope the smallest thing worth shipping.
Frequently asked questions
What Does Small Business Compliance Mean in 2026?
When should a small business buy a compliance tool?
Which compliance workflows can an AI agent run with a person approving?
What are the seven compliance areas every US small business must cover in 2026?
How much does compliance software like Vanta or Drata cost?
What is the best compliance software for SMBs?
Can AI agents automate compliance work for SMBs?
Does an early-stage startup actually need SOC 2 compliance?
How expensive can non-compliance penalties be for a small business?
What happens if my small business is not compliant?
Ready to turn AI into execution?
Book a free assessment of one workflow. We map it, make an honest build versus buy call before any code, and if an off the shelf product covers the job we will tell you so.